Authentication and usage
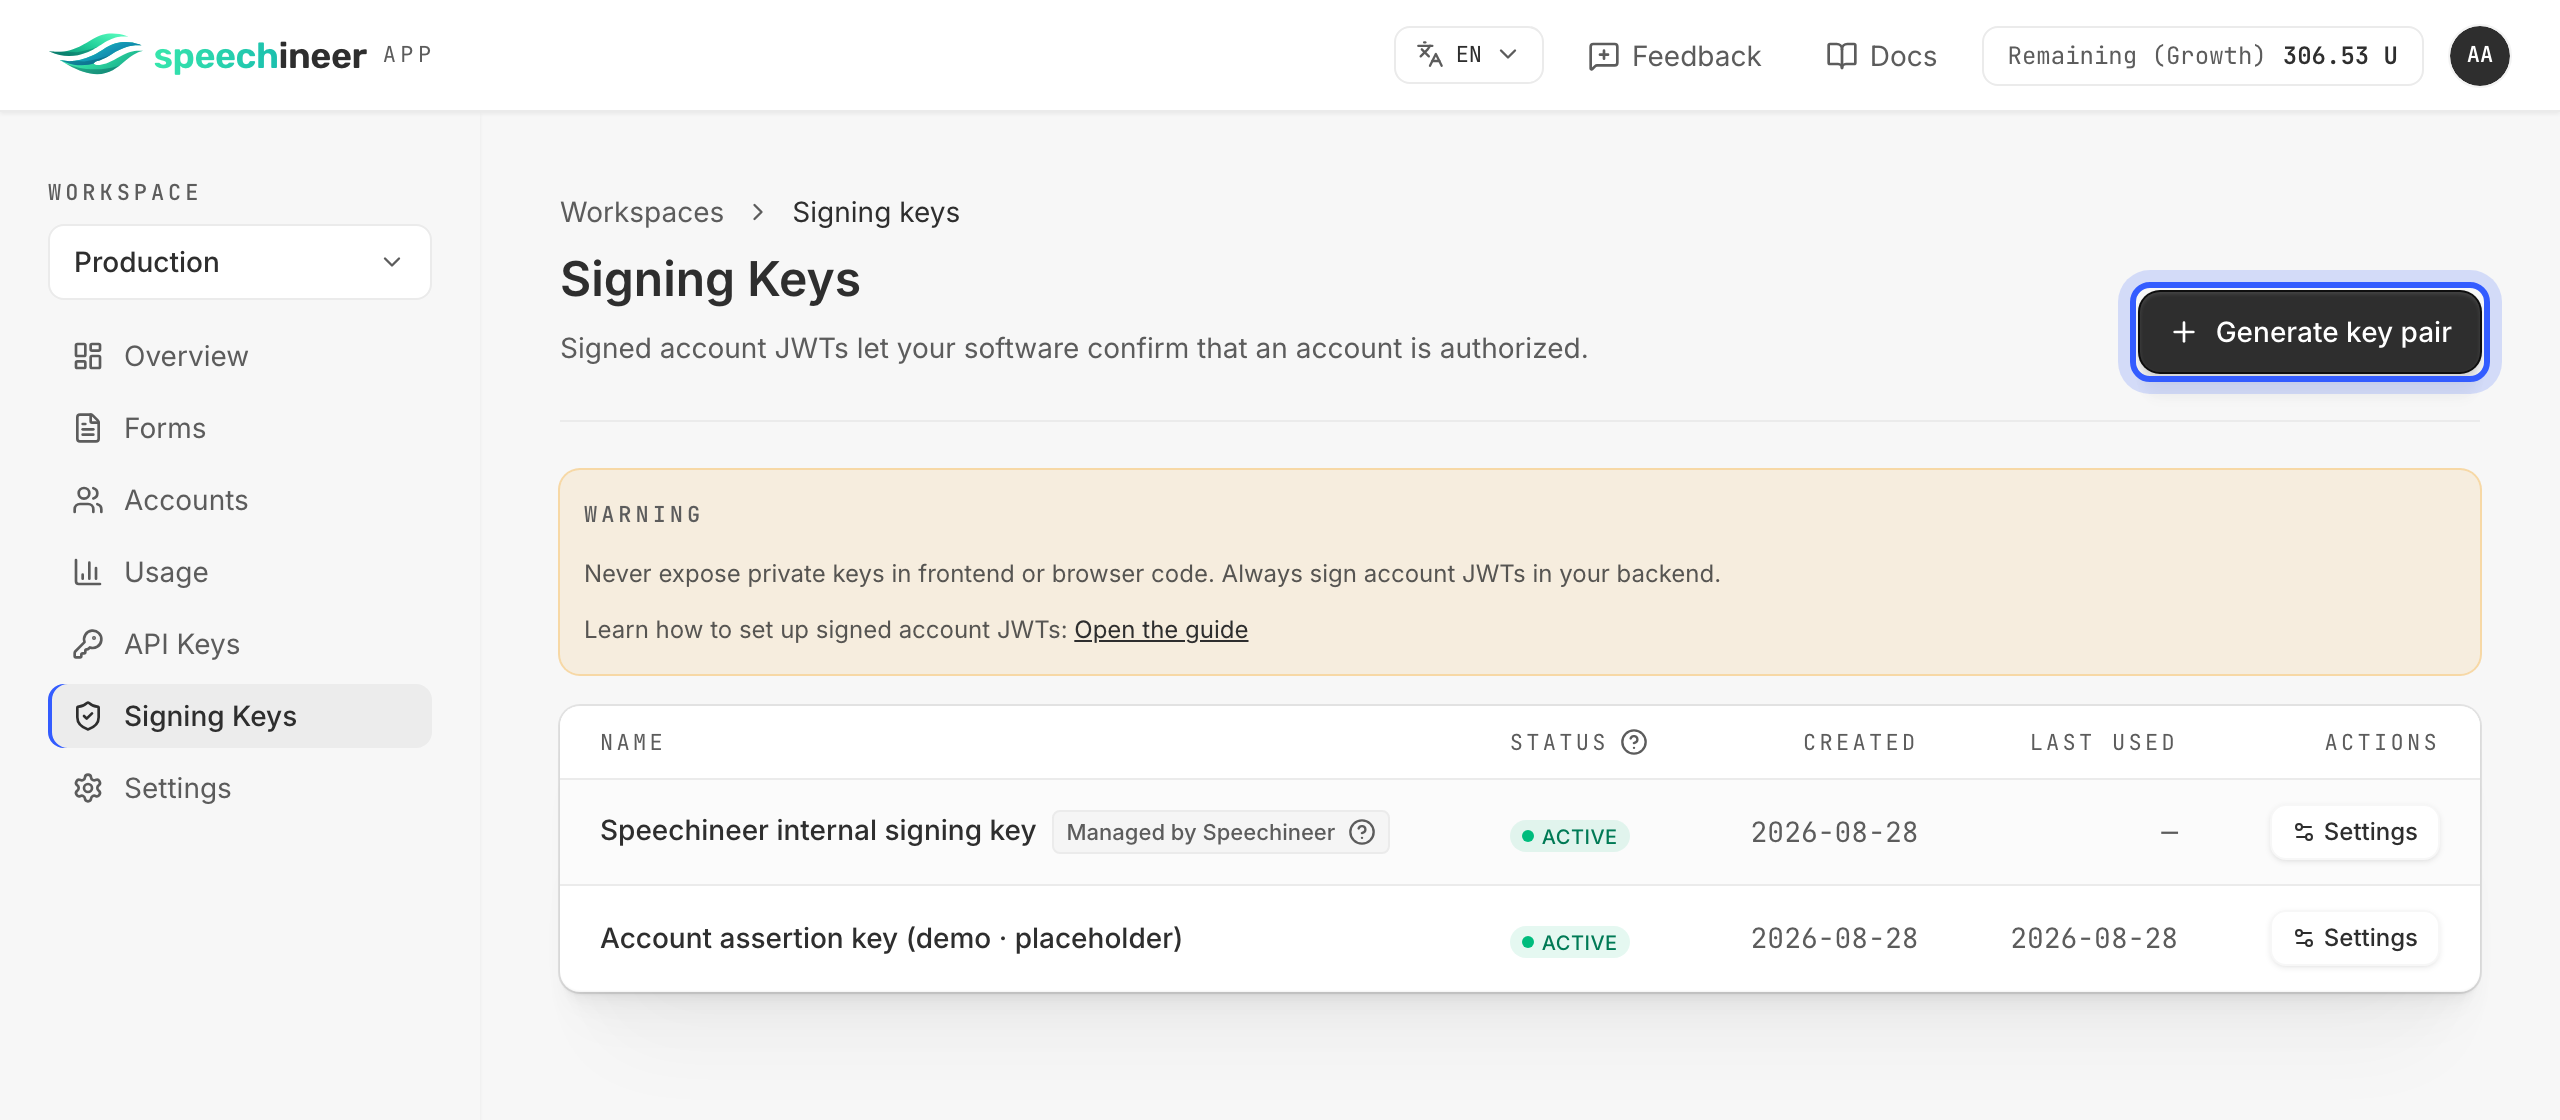
Signing keys
A signing key is a PS256 key pair: the public half lives in your workspace, the private half stays in your backend. With it, your backend signs the tokens that Signed API keys accept — no credential ships to the browser, and the account a session runs for comes from the token, not from the client. Use it for anything behind a login.
In the workspace, Signing keys lists every signing key of the workspace — its name, its status, when it was created and when it was last used. Click Generate key pair and name it: the private key is shown once and never stored, so put it in your backend's secrets right away. The signing key's id, fingerprint and public key stay readable in its settings.
Danger
Additional information in
Name
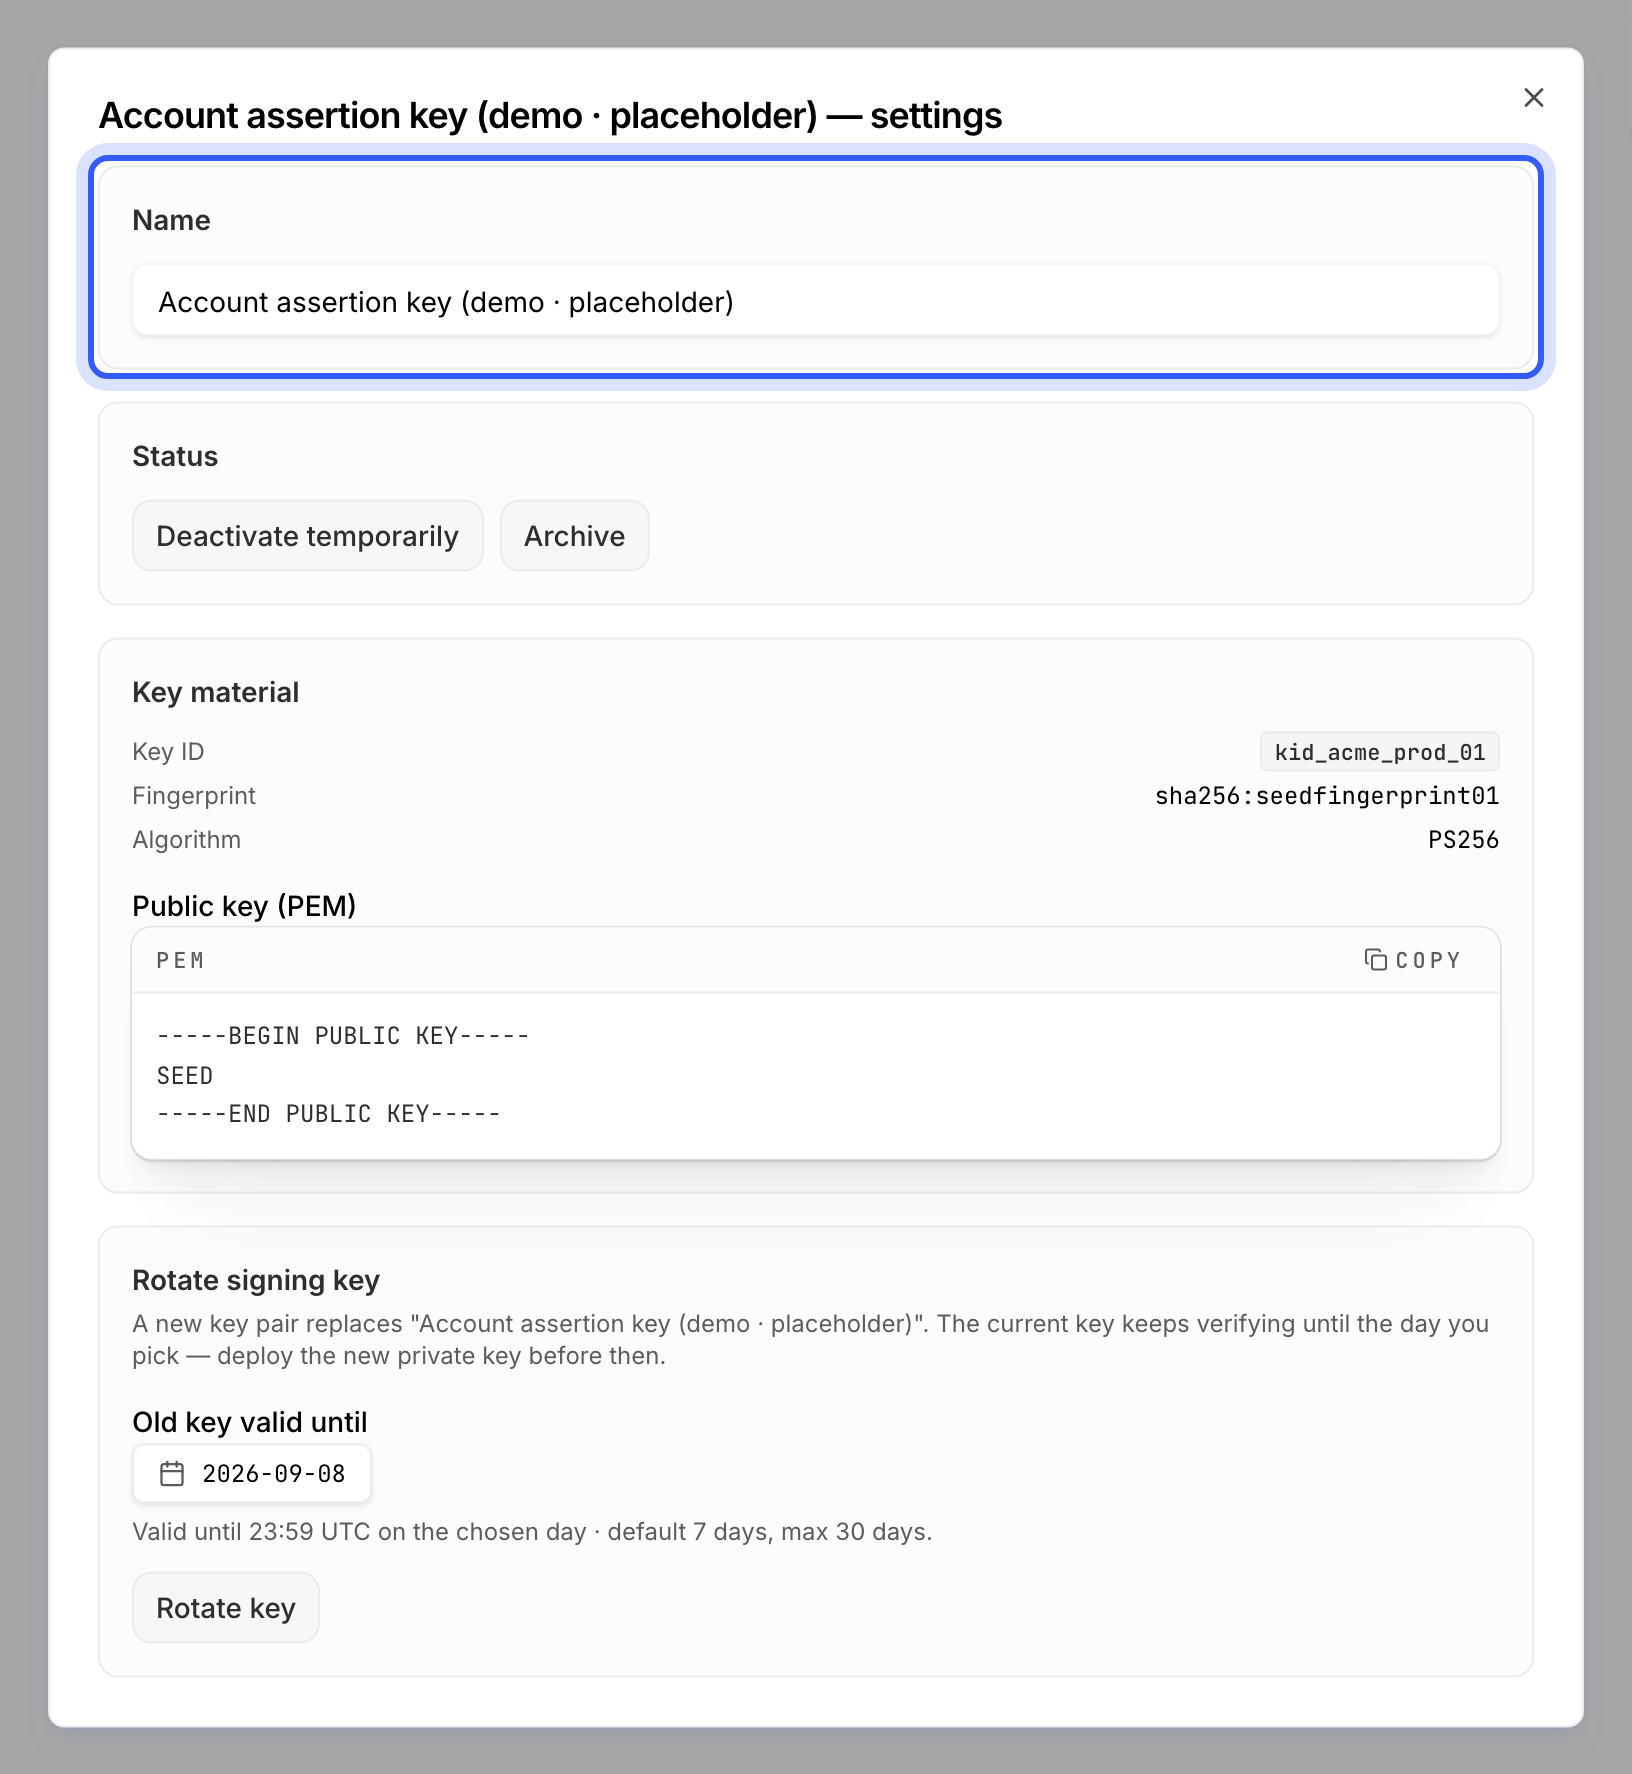
A label for you, shown in the list. Name it after the backend that holds the private half — "Production backend", "Staging backend". Renaming never affects verification.
Status
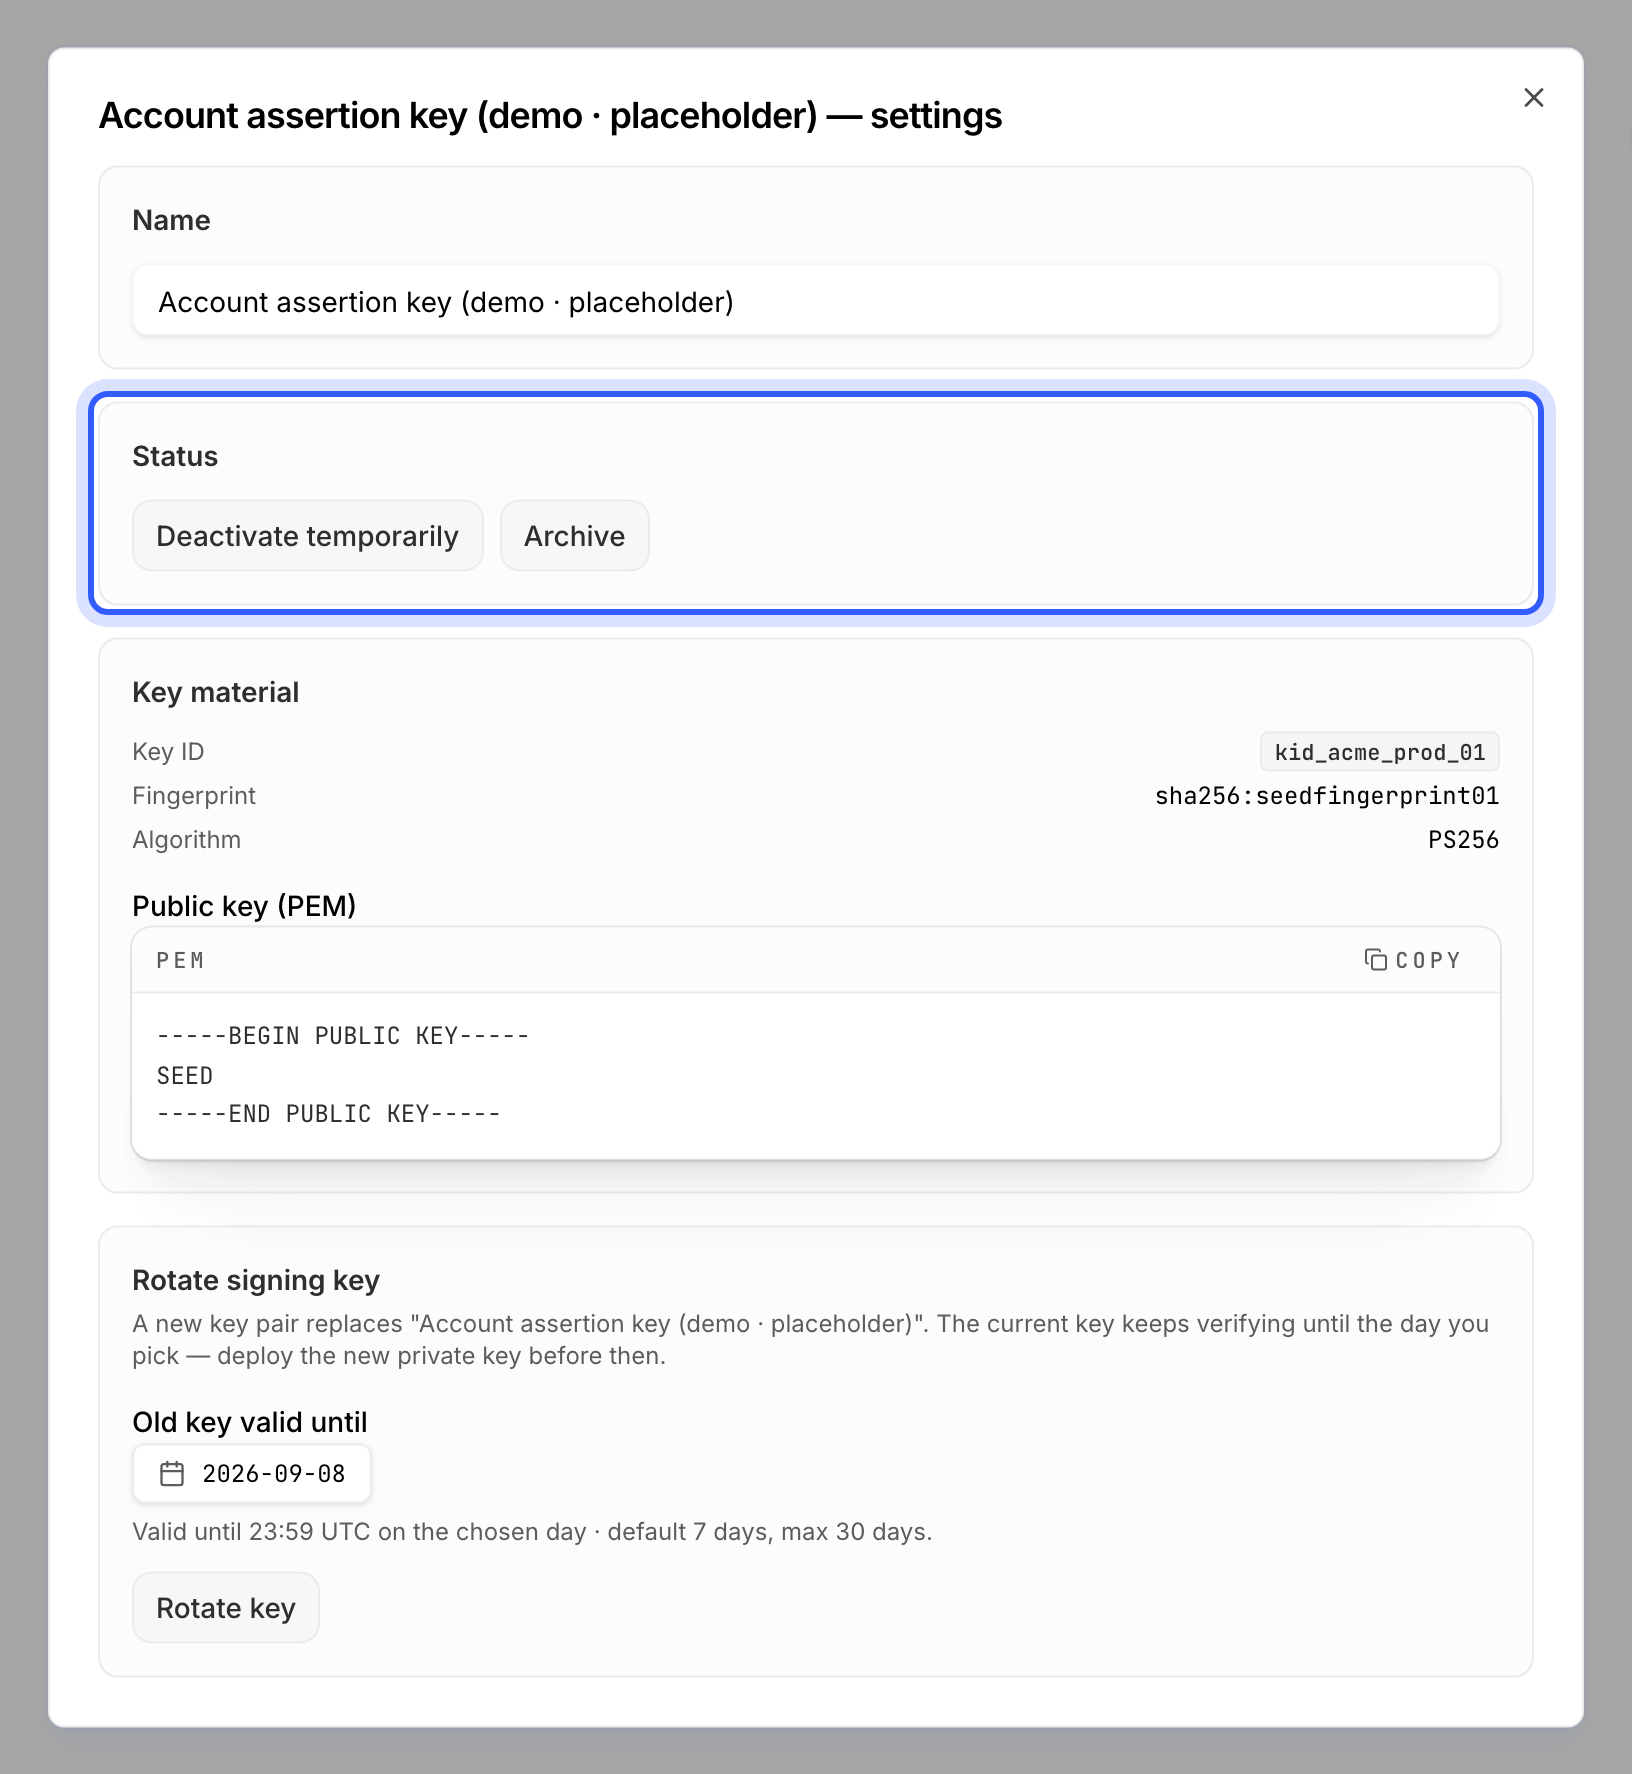
Deactivate temporarily refuses every token signed with this signing key and can be reversed; Archive is final and keeps the history. A signing key rotated out of service archives itself once its deadline has passed.
Rotating a signing key
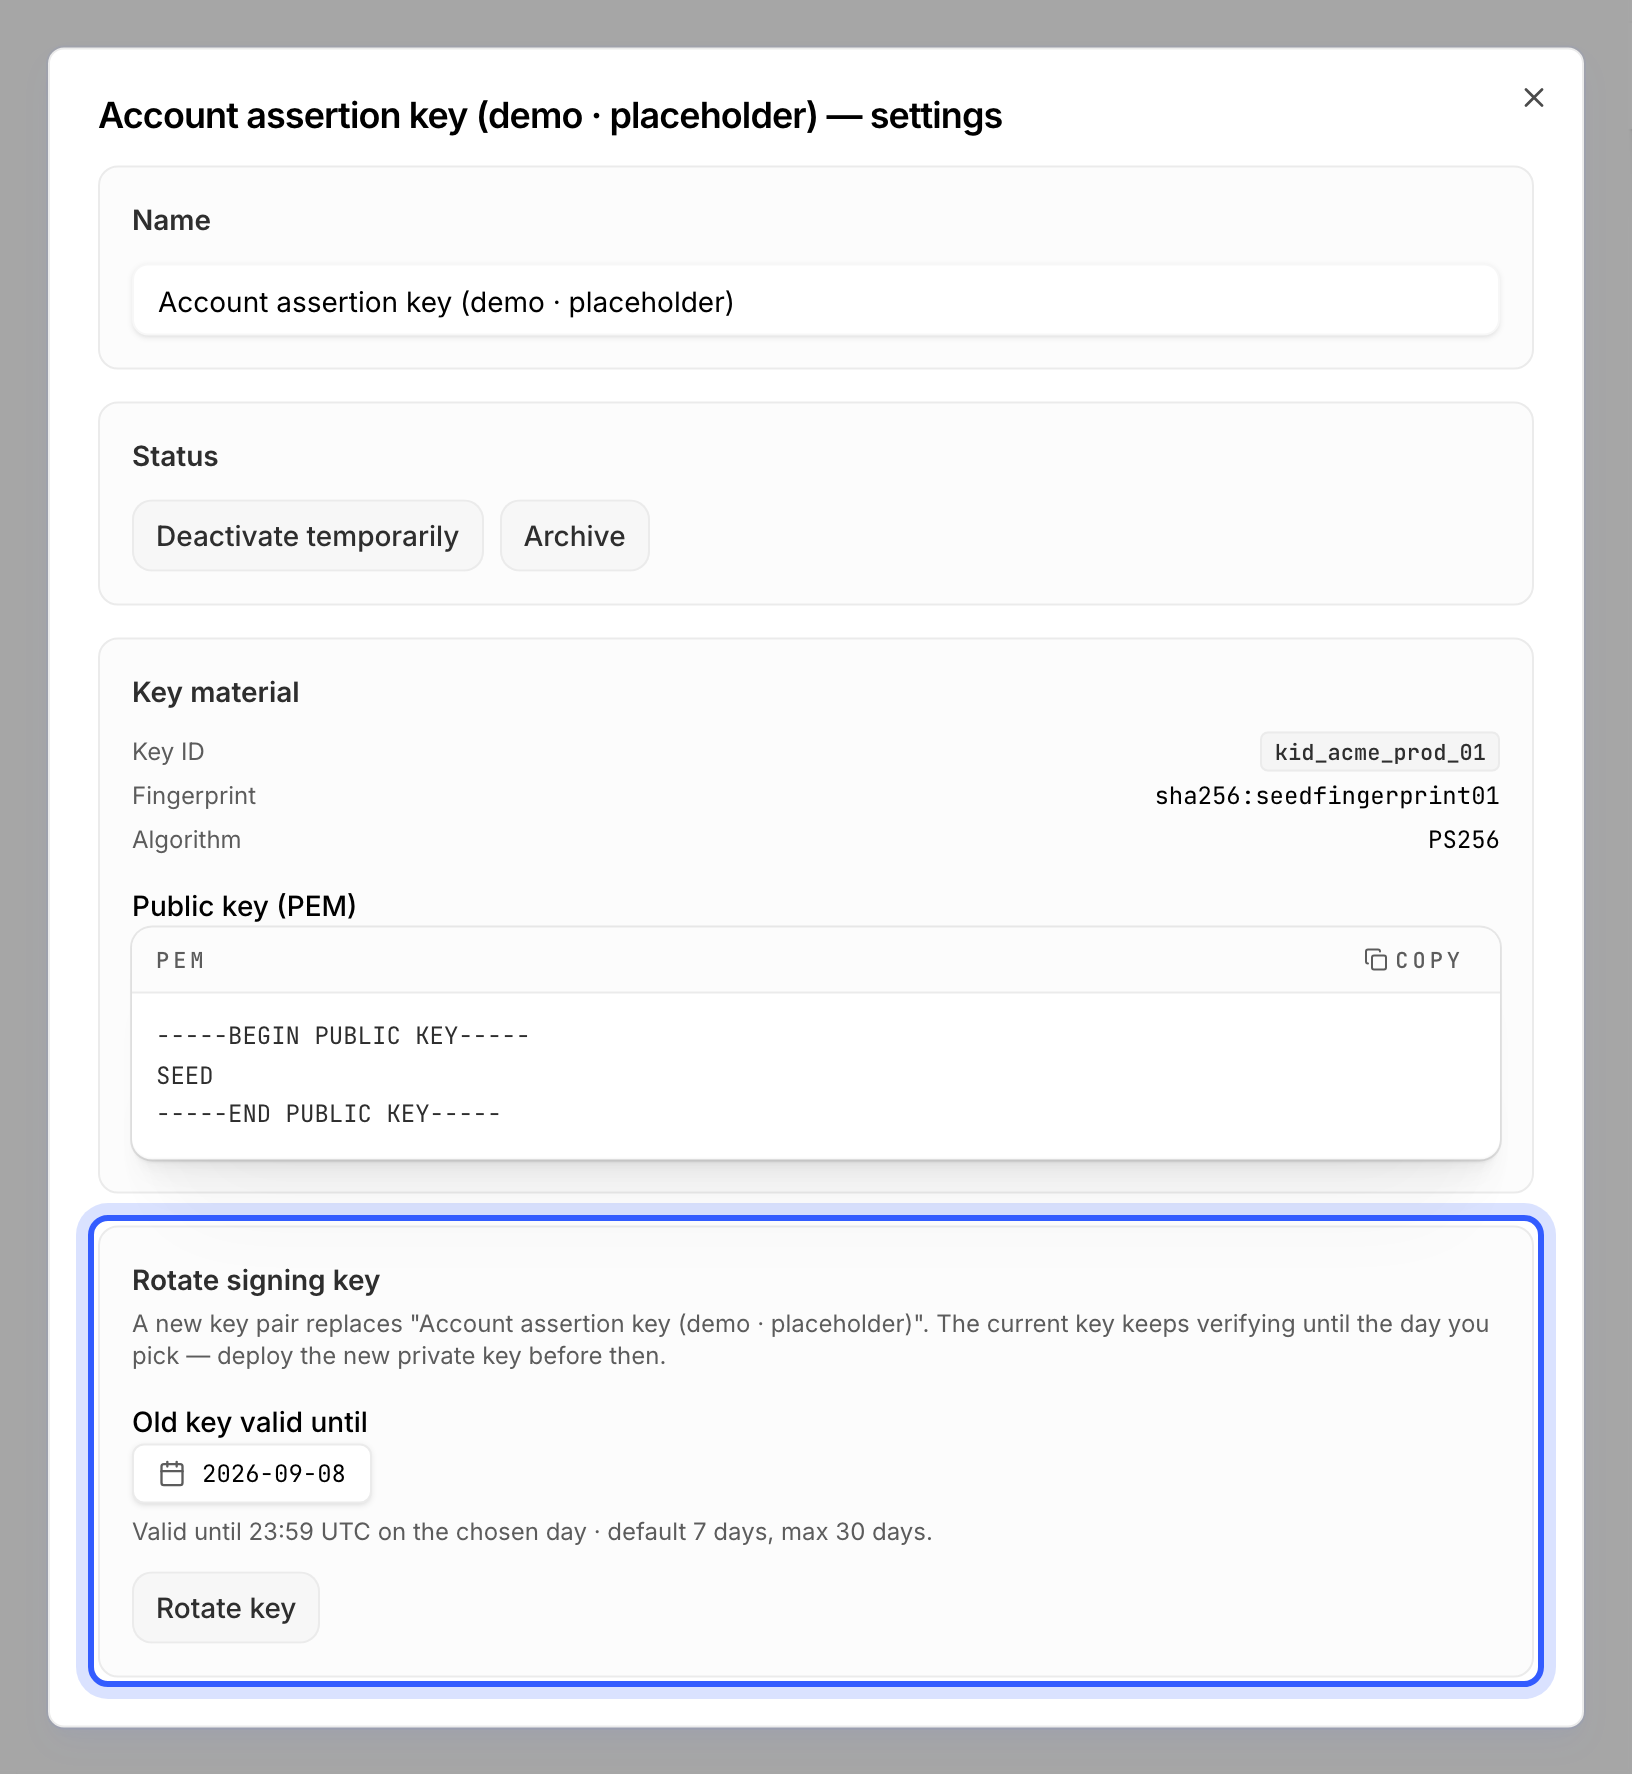
Rotating replaces the key pair. The new pair is created immediately and its private half shown once; the old signing key keeps verifying tokens until a deadline you choose — 7 days by default, 30 at most. Deploy the new private key to your backend before that day: tokens signed with the old key id keep working until the deadline and are refused afterwards, so a deployment never races a key change. Rotate when a private key may have leaked, or on the schedule your security policy sets.